

Coding agentCognitionConfirmed
Story 10 of 16 in the Thursday 19 November editionCognition launches Devin Security Threats for CVE fixes
Live at app.devin.ai/security on 20 November 2026 with Agentic MapReduce repo scanning, Auto-triage and open-source NGINX2Root and Java4Shell fix skills.

 Edited by Ashutosh Shrivastava
20 Nov 2026, 08:30 IST · 2 min read
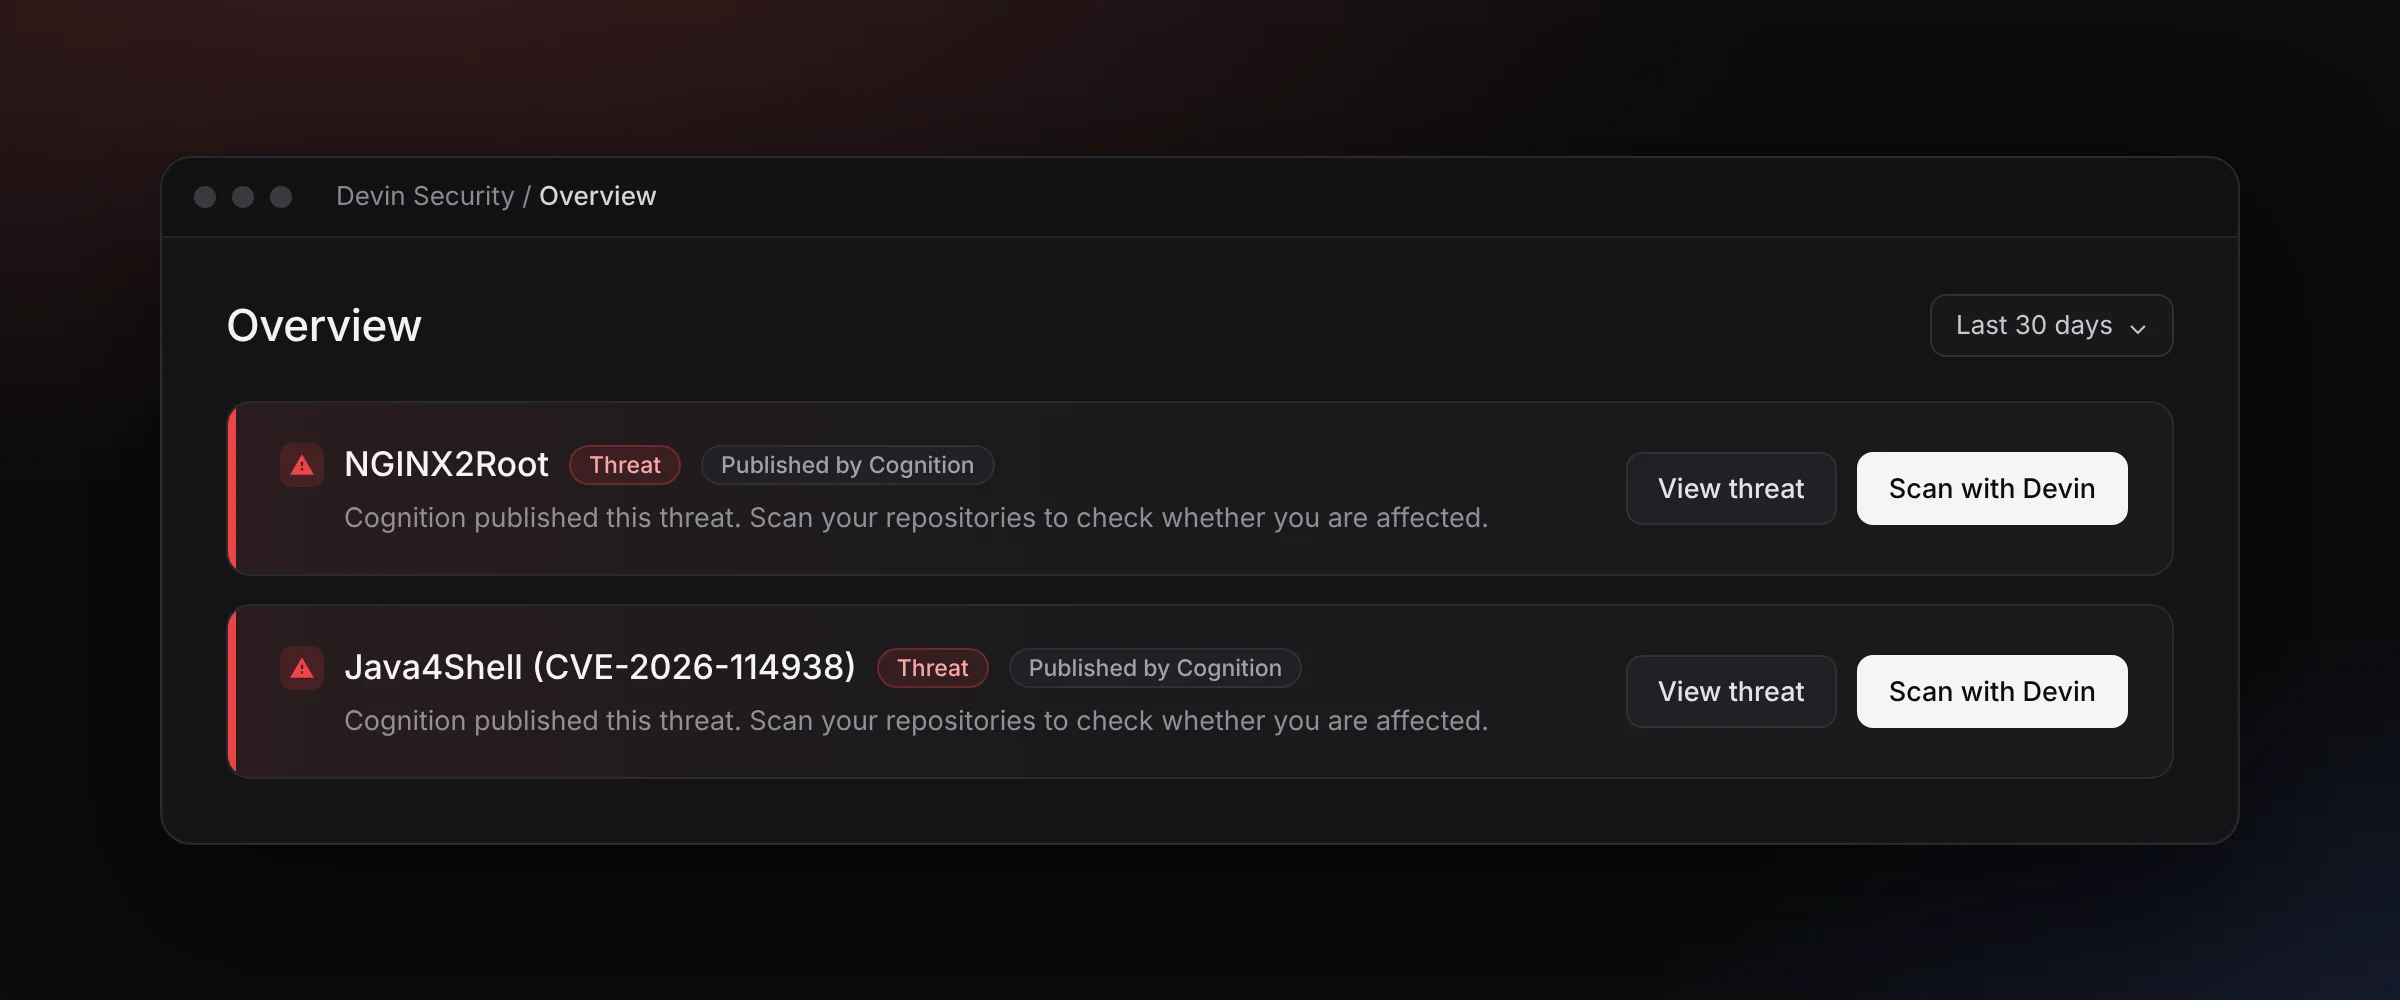
Cognition launched Devin Security Threats (app.devin.ai/security) on 20 November 2026, pairing a managed index of newly disclosed software vulnerabilities with one-click repository scanning and pull-request remediation atop Devin’s Agentic MapReduce engine, expanding the multi-agent platform behind Devin Bots. Selecting Scan with Devin launches a Focus on threats sweep across chosen repositories, ranks findings against the organisation’s threat model and assigns confirmed issues to Devin to draft reviewable fix PRs.
Auto-triage rules, custom internal advisories and open-source fix skills
Security teams can enable Auto-triage with repository lists and minimum severity thresholds so Devin scans automatically whenever Cognition publishes a new advisory (optionally auto-dismissing clean runs), or author custom internal threats from bug bounty reports, vendor notices and incident reviews.
At launch, Cognition published threat definitions alongside open-source plain-Markdown skills (fix-nginx-vuln and fix-java-vuln in the Devin Marketplace Vulnerability Fixes plugin and Devin CLI) targeting Java4Shell (disclosed 17 November 2026) and the five memory-corruption bugs in NGINX2Root (disclosed 18 November 2026).
Technical details
- Dashboard URL and scan engine
- app.devin.ai/security powered by Devin Security Agentic MapReduce
- Initial published advisories
- Java4Shell (17 November 2026 Java runtime RCE) and NGINX2Root (18 November 2026 nginx RCE)
- Open-source Marketplace skills
- fix-nginx-vuln and fix-java-vuln in the Vulnerability Fixes plugin and Devin CLI
Release details & context
Running portable Markdown skills across interactive sessions or external agents
Teams that prefer interactive remediation over batch repository scans can install the Vulnerability Fixes plugin from the Devin Marketplace or Devin CLI and invoke Fix nginx vulnerabilities or Fix Java vulnerabilities directly inside a standard Devin session.
Because Cognition released fix-nginx-vuln and fix-java-vuln as open-source plain-Markdown playbooks, appsec engineers can also read them as human verification checklists or pass them into third-party coding agents.
Cognition release timeline (10 launches tracked)
- Cognition releases Devin Review 2.0 with fivefold cost reduction and faster pull request reviews
Cognition released Devin Review 2.0 for automated pull request reviews, running up to 5 times cheaper and 1.5 times faster than its predecessor.
- Cognition upgrades Devin Teams with free SWE-2 sessions and SSO
Cognition upgrades Devin Teams with included Devin Desktop seats, two concurrent free SWE-2 sessions per user, SAML/OIDC SSO and a standard HIPAA BAA.
- Cognition launches Devin Apps to host private internal web tools
Cognition launches Devin Apps so teams can build, host and share private full-stack web tools directly on Devin’s snapshot-backed cloud machines.
- Cognition launches Devin Bots to lead parallel teams of coding agents
Cognition introduces Devin Bots, persistent manager agents that coordinate parallel Devin sessions and merged roughly 1,600 internal PRs in a week.