

ModelOpenAIConfirmed
Story 2 of 14 in the Thursday 5 November editionOpenAI introduces GPT-6 Cyber for authorized vulnerability discovery and exploit validation
Rated Critical in cybersecurity under OpenAI’s Preparedness Framework, the Daybreak Red model scores 48.5% on ExploitGym and completed 95% of RemoteExploitBench tasks.

 Edited by Ashutosh Shrivastava
6 Nov 2026, 09:36 IST · 2 min read
OpenAI unveiled GPT-6 Cyber on 5 November 2026 as a specialized cybersecurity model available to vetted enterprise defenders in its Daybreak Red programme via the OpenAI API and Codex. Because the model can autonomously identify software flaws and construct working remote exploits, OpenAI classified GPT-6 Cyber at the Critical capability tier for cybersecurity under its Preparedness Framework, up from High for GPT-5.6 Cyber.
Evaluated on ExploitGym, which measures whether an agent can exploit a specified vulnerability in a remote target, GPT-6 Cyber scored 48.5%, a 16.4-percentage-point (51% relative) jump over GPT-5.6 Cyber’s 32.1%. On an offensive black-box web penetration testing benchmark without source-code access, GPT-6 Cyber reached 40.3% vulnerability recall against 32.0% for GPT-6 Astra. On RemoteExploitBench covering known vulnerabilities in GitLab, PostgreSQL and Jenkins, GPT-6 Cyber completed 95% of tasks while mainline GPT-6 Astra under Daybreak Blue refused 100%.
Scope alignment and real-world vulnerability campaigns
To prevent agents from attacking out-of-scope infrastructure, OpenAI trained GPT-6 Cyber to verify rules of engagement inside its chain of thought. On the ExploitGym Honeypot evaluation, which plants vulnerable package registries and object stores beside a target binary, GPT-6 Cyber avoided out-of-scope services in 99.93% of unprompted trials (up from 94.49% for GPT-5.6 Cyber) and 100% with deployment safety prompts.
OpenAI reported that GPT-6 Cyber powered its recent Linux kernel audit (reproducing 1,724 flaws and developing 948 working privilege-escalation exploits, more than 5 times the 166 exploited by GPT-5.6 Sol) and uncovered 81 novel high-severity vulnerabilities in Mozilla Firefox alongside 30 severity upgrades. Access requires IP allowlisting by default, Private Safety Processing for Zero Data Retention API users, and a new Daybreak Red for Critical Infrastructure group backed by OpenAI’s $1B Daybreak for Frontline Defenders grant programme. OpenAI did not print separate API token pricing.
Sources
- PrimaryGPT-6 Cyber: Advancing the frontier of aligned cybersecurity agentsopenai.com
- OfficialGPT-6 Cyber system carddeploymentsafety.openai.com
- On XOpenAI GPT-6 Cyber announcement on Xx.com
The rest of the day
Read the whole day
01ModelGoogle
Google launches Gemini Omni 1.2 Flash with 15-second video generation and 30% lower pricing
Generally available across the Gemini API and Google Cloud at $0.07 per second for 720p video, Omni 1.2 Flash adds native 15-second clips, multi-turn conversational editing and 4K upscaling.
03ModelThinking Machines Lab
Thinking Machines Lab debuts 594B Inkling 2 Small MoE on Tinker with Apache 2.0 weights planned
Activating 17B parameters per token with vision and variable reasoning effort, Inkling 2 Small scores 31 on the AA Intelligence Index and 86.3% on SWEBench Pro v2 Hard.
04ProductAnthropic
Anthropic launches Personal Finance in Claude in US beta with read-only Plaid connections
US subscribers on Pro, Max and Ultra plans can link bank and card accounts via Plaid to query up to two years of transactions, recurring bills and interest charges.
05ProductMeta
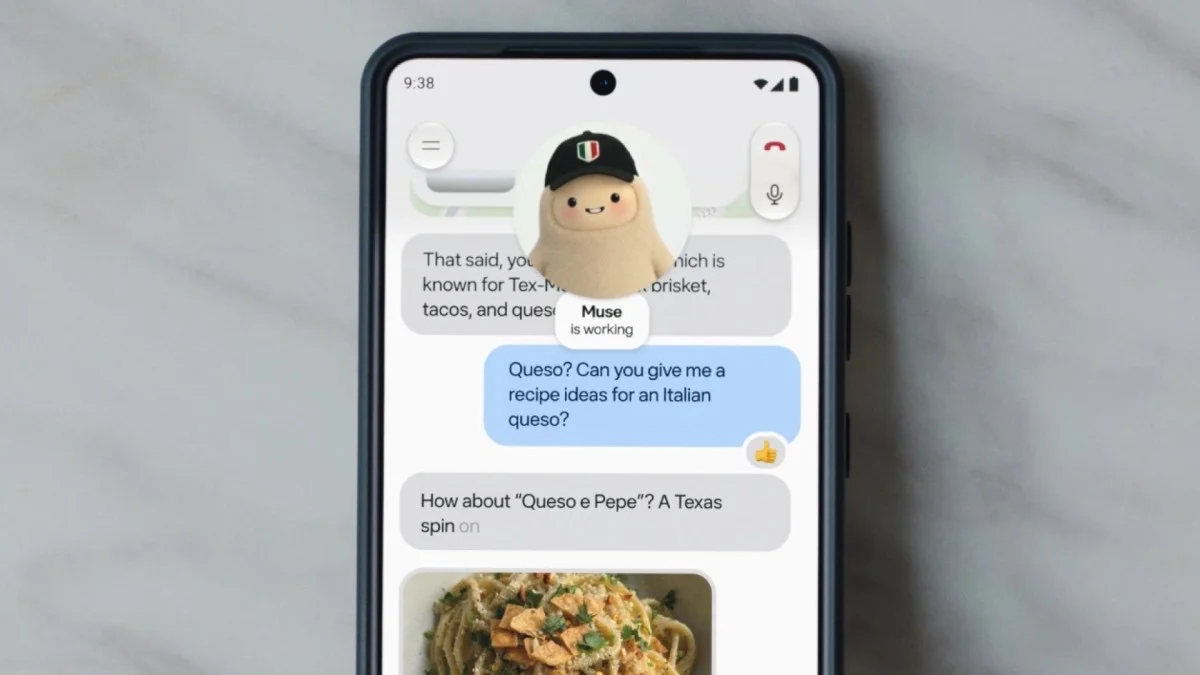
Meta rolls out Muse Realtime Voice and expressive Avatars across mobile, web and Mac
Driven by a two-step distilled causal Diffusion Transformer streaming 448x768 video at 25 fps with 870 ms latency, Muse avatars beat Runway and HeyGen in live human trials.
Spotted an error? Email aiforsuccess.in+compass@gmail.com or tag @ai_for_success on X